ISO 13485 internal audit checklist, with what the FDA QMSR adds.
Ten audit areas, from design transfer to complaint handling, each with
the records to sample, questions for the people doing the work, red
flags and ISO 13485:2016 clause numbers. Each area notes what 21 CFR
Part 820 adds for devices marketed in the US.
ISO 13485:2016, the current edition and the one the QMSR incorporates by reference.
Organized by
Area, the way an auditor walks a site. ISO 13485 is copyrighted, so clauses appear as numbers only.
Cost
Nothing. The checklist needs no email. The fillable Excel toolkit is free too; we ask for your name, company and email.
To print
What clause 8.2.4 asks of your audit program
ISO 13485 puts internal audit in clause 8.2.4. In our words, a
certification auditor will look for:
A documented procedure setting out who plans, conducts, records and reports audits.
A program based on risk and history: how much each process matters, how it is performing, and what earlier audits found.
A recorded basis for each audit: what it is measured against, what it covers, how often it happens and how it is done.
Objective auditors who do not audit their own work.
Records of each audit: what was covered, what was found and what the auditor concluded.
Prompt action by the managers of the area audited, then a follow-up that checks the actions were taken and reports what it found.
No clause sets a frequency. Rate each process on risk to patients and
users, regulatory exposure, complexity, recent problems and recent
change, and audit the higher-rated ones more often. A defensible
default: every process once a year. New to the subject? Start with
our glossary entry on internal audit.
How to sample
Every audit is a sample; certification audit reports must say so. How
you sample sets what your conclusions are worth.
Define the population: every complaint, lot, design change or CAPA since the last audit.
Pick the sample yourself. A sample the auditee hands you is a showcase.
Spread it across shifts, device families, people, and old and recent records.
Start small, then expand. Start with three to five records. When one fails, take more: that tells a slip from a system failure.
Trace both ways: from a complaint back to the lot, its components and its release, and from a supplier change forward to the devices it reached.
Record what you sampled, by ID, so anyone can find it again.
Free download · Excel + PDF
Get this checklist in Excel, plus the rest of your audit program
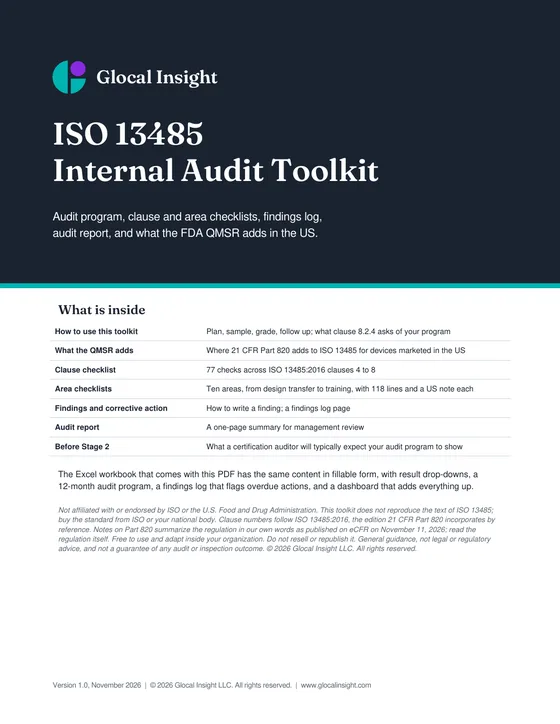
The ISO 13485 Internal Audit Toolkit: this checklist as an 18-sheet Excel workbook and a 20-page printable PDF, plus what goes around it.
A 12-month audit program and a one-page audit plan
A clause checklist: 77 checks across clauses 4 to 8, with a column for what 21 CFR Part 820 adds
Ten area checklists with result drop-downs, from design transfer to training
A findings log that flags overdue corrective actions
A dashboard that totals findings and results by sheet, and a one-page report for management review
Excel (.xlsx, no macros) and PDF. Free to use and adapt inside your organization. Not affiliated with ISO or FDA; it does not reproduce the standard.
Thanks. Your files are ready:
Save the Excel file before you fill it in, then open the Start Here sheet. Questions? Write to info@glocalinsight.com.
118 lines in ten areas; management review (5.6) and the audit program itself are in the toolkit's clause checklist. Use it as an aid, not a limit: follow
the evidence where it leads. Checkboxes are not saved, so print the
page or save it as a PDF.
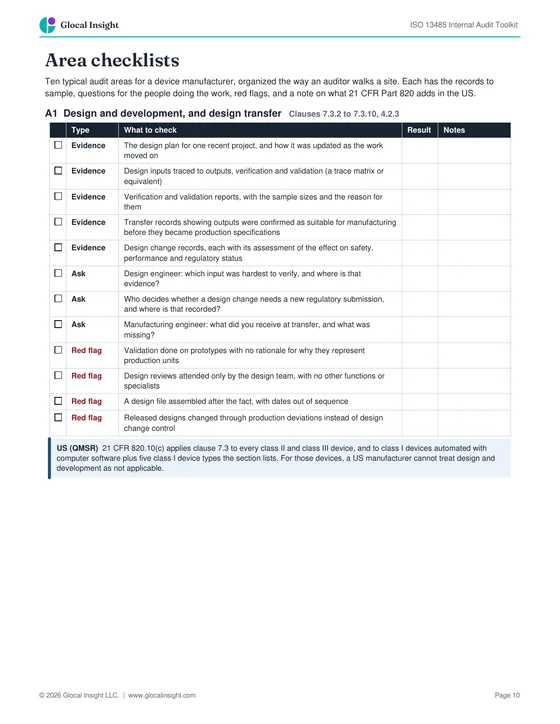
1. Design and development, and design transfer
Clauses: 7.3.2 to 7.3.10, 4.2.3
US (QMSR): 21 CFR 820.10(c) applies clause 7.3 to every class II and class III device, and to class I devices automated with computer software plus five class I device types the section lists. For those devices, a US manufacturer cannot treat design and development as not applicable.
US (QMSR): The QMSR keeps ISO 13485's term "safety and performance", but 21 CFR 820.3 says the term does not reduce the obligation to provide reasonable assurance of safety and effectiveness. Most manufacturers use ISO 14971 as their risk management method; ISO 13485 refers to it in a note rather than requiring it.
US (QMSR): FDA can now inspect supplier audit reports: the QMSR did not keep the exception in former 21 CFR 820.180(c). Under 820.1(a)(2) the regulation does not apply to manufacturers of components or parts, so your purchasing controls are how their quality reaches the finished device.
US (QMSR): 21 CFR 820.45 adds labeling and packaging controls to clause 7.5.1: documented procedures; labeling and packaging examined for accuracy (UDI, UPC or other device identification, expiration date, storage, handling and any additional processing instructions) before release or storage, where applicable; labeling release documented; and labeling and packaging inspected before use to prevent mix-ups.
US (QMSR): 21 CFR 820.10(b) ties clause 7.5.8 to unique device identification under Part 830, and clause 7.5.9.1 to device tracking under Part 821 where it applies. 820.10(d) extends the implantable-device traceability of 7.5.9.2 to devices that support or sustain life and whose failure, when used as labeled, could reasonably be expected to cause significant injury. 820.35(c) requires the UDI to be recorded for each device or batch.
US (QMSR): 21 CFR 820.10(b) requires complaints that meet Part 803 (medical device reporting) to be reported to FDA, and advisory notices under clauses 7.2.3, 8.2.3 and 8.3.3 to follow Part 806 (corrections and removals). 820.35(a) lists what reportable and investigated complaint records must hold (device name, date received, UDI or UPC, complainant contact, details, any correction or corrective action, any reply) and requires a documented justification when a similar complaint makes a new investigation unnecessary. 820.35(b) lists what servicing records hold.
US (QMSR): No QMSR section supplements clauses 8.4 or 8.5; FDA inspects CAPA against the ISO 13485 clauses as incorporated. Internal audit reports are now open to FDA inspection, so an audit finding left without action is visible to an FDA investigator as well as to your certification body.
US (QMSR): 21 CFR 820.10(b) ties clause 8.3.3 (nonconforming product found after delivery) to Part 806: a correction or removal may have to be reported to FDA, and one that is not reported still needs a record.
US (QMSR): 21 CFR 820.35 supplements clause 4.2.5 for complaint, servicing and UDI records, and lets you mark records as confidential to help FDA decide on disclosure. FDA can now inspect management review, internal audit and supplier audit reports (FDA, QMSR FAQ).
From glocalinsight.com/resources/iso-13485-internal-audit-checklist/,
last verified November 11, 2026. The toolkit adds a clause-by-clause
list of 77 audit questions for clauses 4 to 8.
What the QMSR adds to ISO 13485
FDA's Quality Management System
Regulation took effect on February 2, 2026. It
amends 21 CFR Part 820 and incorporates ISO 13485:2016 by reference,
so for a US manufacturer the clauses above are also the regulation.
Part 820 then adds a short list of US requirements. Our summary:
Part 820
What it adds
ISO 13485 clauses
21 CFR 820.1
Scope: finished-device manufacturers. Does not apply to manufacturers of components or parts. Where ISO 13485 conflicts with the FD&C Act or FDA's regulations under it, the Act and those regulations control.
Whole system
21 CFR 820.3
Definitions. Using "safety and performance" does not reduce the obligation to provide reasonable assurance of safety and effectiveness.
Whole system
21 CFR 820.10(b)
UDI under Part 830; tracking under Part 821 where it applies; reporting under Part 803; corrections and removals under Part 806.
7.2.3, 7.5.8, 7.5.9.1, 8.2.3, 8.3.3
21 CFR 820.10(c)
Design and development applies to class II and III devices and to listed class I devices (software-automated plus five device types).
7.3
21 CFR 820.10(d)
Implantable-device traceability also applies to devices that support or sustain life and whose failure, when used as labeled, could reasonably be expected to cause significant injury.
7.5.9.2
21 CFR 820.35
Content of complaint, servicing and UDI records; records may be marked confidential.
4.2.5, 7.5.4, 7.5.8, 7.5.9, 8.2.2
21 CFR 820.45
Labeling and packaging: procedures, accuracy check before release or storage, documented release, and documented inspection before use to prevent mix-ups.
7.5.1
FDA QMSR FAQ
FDA can inspect management review, quality audit (internal audit) and supplier audit reports; the former 820.180(c) exception is gone.
5.6, 7.4, 8.2.4
One change matters most to an internal audit program. The old
regulation excepted internal audit reports from FDA inspection
(former 21 CFR 820.180(c)). FDA now
states that the QMSR gives it “the authority to inspect
management review, quality audits, and supplier audit reports.”
Write every report and finding as a record someone outside the
company will read.
FDA does not require or issue ISO 13485 certificates, and a
certificate does not exempt a manufacturer from inspection. Where
certification fits, and what it costs, is in our
ISO 13485 certification cost guide.
How to write a finding
A finding has three parts. If one is missing, the process owner cannot
act on it, and no one reading the report later can rely on it.
The requirement. An ISO 13485 clause, your own procedure, a regulation such as 21 CFR Part 820, or a customer requirement. No requirement, no nonconformity.
The evidence. Enough detail that someone else could find what you saw: IDs, dates, lots, places.
The statement. A sentence or two about the system, not a retelling of the evidence.
Example
Requirement: Each complaint file records the decision on whether the complaint must be reported to a regulator, and why (8.2.2; procedure QP-14). US records of reportable or investigated complaints hold any UDI or UPC (21 CFR 820.35(a)).
Evidence: Complaints C-26-041 and C-26-057 (leaking connector, lot 2611) have no recorded reportability decision, and C-26-057 has no UDI. 2 of 8 complaint files sampled.
Statement: Complaint files do not consistently record the reportability decision or the device identifier.
Do not soften a nonconformity into an observation. Leave the cause and
the fix to the process owner, then check that the corrective action
worked before you close it (8.5.2). Our page on
major nonconformities
explains where minor ends and major begins, and our glossary entry on
CAPA covers the loop that follows.
Before Stage 2
Stage 1 checks that internal audits and management reviews are being
planned and performed, and Stage 2 examines both. Tick every line
before you book it. No one on staff independent of the work? Our
independent internal audits
fill that gap. How long will the certification audit take? Our
ISO 13485 audit days calculator estimates it.
Who reads your internal audits
Accredited certification bodies work to ISO/IEC
17021-1:2015, and since February 2026 FDA can read the
reports too.
Initial certification. Stage 1 checks that internal audits and management reviews are planned and performed, and Stage 2 includes both.
Every certification audit report. It must summarize the evidence on your internal audit and management review process.
Every surveillance audit. Internal audits and management review head the list of what each must include.
FDA inspections. Management review, quality audit and supplier audit reports are no longer exempt from inspection under the QMSR.
If an outside auditor finds in two days what your program missed in a
year, expect questions about the program itself. Our
internal auditor training covers
sampling and writing findings, and our
ISO 13485 consulting builds the
system the audits test, with the QMSR additions built in.
Common questions
What should an ISO 13485 internal audit checklist include?
The records to sample, the questions to ask the people doing the work, and the conditions that would be findings, for each process in scope, with the clause numbers and the regulatory requirements of your markets. For a US manufacturer that means the additions in 21 CFR Part 820 as well as the ISO 13485 clauses.
How often do ISO 13485 internal audits have to be done?
Clause 8.2.4 asks for audits at planned intervals, under a program that reflects how much each process matters, how it is performing and what earlier audits found. It sets no fixed frequency. A defensible default is every process in scope once a year, with processes that carry more risk to patients or have a history of problems audited more often.
Who can perform an ISO 13485 internal audit?
Anyone competent who does not audit their own work: a trained employee from another department, a colleague from another site, or an outside auditor. ISO 13485 requires a documented internal audit procedure, and certification auditors check that your auditors were objective and competent.
Can FDA see our internal audit reports under the QMSR?
Yes. FDA states that the QMSR gives it the authority to inspect management review, quality audit and supplier audit reports, and that the exceptions in the former 21 CFR 820.180(c) were not carried over. Write reports and findings as factual records, and close the loop on each finding.
Does FDA require ISO 13485 certification?
No. Since February 2, 2026, 21 CFR Part 820 incorporates ISO 13485:2016 by reference, so a US manufacturer has to meet the standard's requirements, but FDA does not require or issue ISO 13485 certificates, and a certificate does not exempt a manufacturer from inspection.
Should the internal audit cover 21 CFR Part 820 as well as ISO 13485?
If you market devices in the US, yes. Part 820 adds requirements for labeling and packaging and for complaint, servicing and UDI records, makes design controls mandatory for class II and III and some class I devices, and ties several clauses to other FDA rules: medical device reporting (Part 803), corrections and removals (Part 806), tracking (Part 821) and unique device identification (Part 830). Put them in the audit criteria for the processes they touch.
Do we need an internal audit before the certification audit?
Yes. Under ISO/IEC 17021-1, Stage 1 must evaluate whether internal audits and management reviews are being planned and performed, and Stage 2 includes both. Every surveillance audit reviews them again.
2026-11-11 — Published, with the free ISO 13485 Internal Audit Toolkit (Excel and PDF). QMSR notes checked against 21 CFR Part 820 on eCFR and FDA's QMSR FAQ. ISO's page for ISO 13485:2016 checked: last reviewed and confirmed in 2025, still current.