
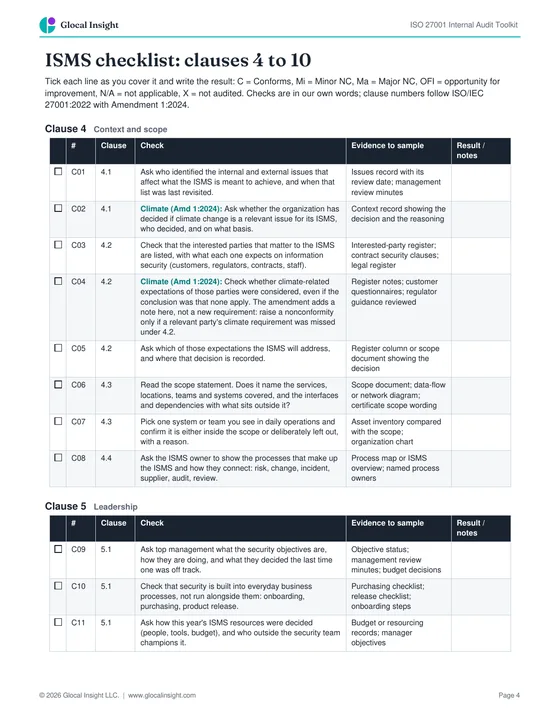
Clause 4: Context and scope
Notes: ____________________________________________________________
Free checklist · Printable · Excel toolkit below
52 checks across clauses 4 to 10 of ISO/IEC 27001:2022, in our own words, each with the evidence to sample. Then a sampling guide to all 93 Annex A controls by theme, and a way to tie every finding back to your Statement of Applicability.
Last verified November 11, 2026
Internal audit sits in clause 9.2, split into 9.2.1 (the purpose of the audits) and 9.2.2 (the audit program). In short, and in our own words:
The standard sets no frequency and names no method. ISO/IEC 27007:2020 and ISO 19011:2026 give optional guidance on auditing an ISMS. New to the subject? Start with our glossary entries on the ISMS and internal audit.
A certification auditor will ask why each part of the ISMS gets the attention it does. Answer with your risk assessment and your earlier audit results.
Every audit is a sample. With an ISMS, the population is your Statement of Applicability, and the evidence lives in systems as much as in documents.
Free download · Excel + PDF
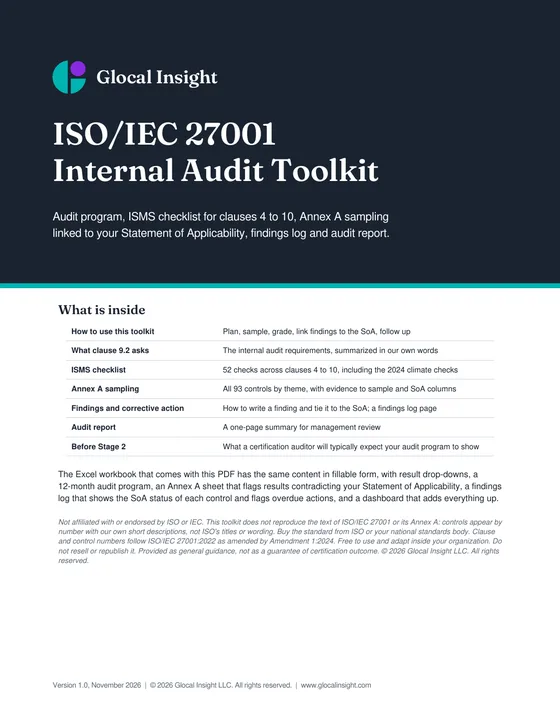
The ISO 27001 Internal Audit Toolkit: this checklist as a 9-sheet Excel workbook and a 16-page printable PDF, plus what goes around it.
Excel (.xlsx, no macros) and PDF. Free to use and adapt inside your organization. Not affiliated with ISO or IEC; it does not reproduce the standard or its control titles.
Thanks. Your files are ready:
Save the Excel file before you fill it in, then open the Start Here sheet. Questions? Write to info@glocalinsight.com.
Want an auditor from outside your team? We run internal audits on site and remotely. See our independent internal audits
Auditor: ____________________ Auditee / area: ____________________ Date: __________ SoA version: ______
Use it as an aid, not a limit: follow the evidence where it leads. Checkboxes are not saved, so print the page or save it as a PDF.
Notes: ____________________________________________________________
Notes: ____________________________________________________________
Notes: ____________________________________________________________
Notes: ____________________________________________________________
Notes: ____________________________________________________________
Notes: ____________________________________________________________
Notes: ____________________________________________________________
From glocalinsight.com/resources/iso-27001-internal-audit-checklist/, last verified November 11, 2026. Clause numbers follow ISO/IEC 27001:2022 with Amendment 1:2024.
Annex A of ISO/IEC 27001:2022 groups its controls into four themes. Each line gives the control number, what it covers in our own words (not ISO's title), and the evidence worth sampling. Test the ones your Statement of Applicability says apply, and a few it excludes.
A finding has three parts: the requirement, the evidence and the statement of what is missing. In an ISMS, add a fourth: what it means for the Statement of Applicability and the risk register. Certification auditors compare the SoA with what they see, so an SoA that still says implemented after your own audit found a gap becomes a second finding.
Example
Requirement: Backup standard BK-02: each production database is restored in a test at least once a quarter (A.8.13).
Evidence: Restore test records for Q2 and Q3 2026 exist for 1 of 3 production databases; the other two were last restored in a test in March 2026.
Statement: Restore testing is not carried out at the interval the backup standard sets.
SoA and risk: SoA version 3 marks A.8.13 implemented: review the status and the related risk entry.
The toolkit's Annex A sheet compares each result with the SoA status you copy in, and flags five patterns:
Leave the cause and the fix to the control owner, and check that the corrective action worked before closing it. Our page on major nonconformities explains where minor ends and major begins.
Stage 1 checks that internal audits and management reviews are being planned and performed, and Stage 2 examines both. Tick every line before you book it. No one on staff independent of the work? Our independent internal audits fill that gap. How long will the certification audit take? Our ISO 27001 audit days calculator estimates it.
Accredited certification bodies work to ISO/IEC 17021-1:2015, and to ISO/IEC 27006-1:2024 for ISMS audits.
If a certification auditor finds in a few days what your program missed in a year, expect questions about the program itself. Our internal auditor training covers sampling and writing findings, and our ISO 27001 consulting includes a first internal audit run by us. Budgeting for certification? See what ISO 27001 certification costs.
Two parts. Checks on the management system, clauses 4 to 10: context and scope, leadership, risk assessment and treatment, the Statement of Applicability, objectives, support, operation, monitoring, internal audit, management review and corrective action. And a sampling plan for the Annex A controls your Statement of Applicability says apply, tested in the systems themselves. Ours has 52 clause checks and a line for each of the 93 Annex A controls.
ISO/IEC 27001 asks for internal audits at planned intervals and sets no fixed frequency. Clause 9.2.2 bases the program on how important each process is and on the results of earlier audits. A common pattern is the whole ISMS at least once a year, with higher-risk areas more often, and every applicable Annex A control covered across the program.
The standard does not say so. It requires your Statement of Applicability to account for all 93 controls, and your audit program to cover the ISMS. Before the first Stage 2 audit, aim to have audited clauses 4 to 10 and the applicable controls. After that, a program that covers every applicable control within the certification cycle, and the higher-risk ones every year, is easy to defend.
Anyone competent who can be objective and impartial about the area audited: a trained employee from another team, a peer from another site, or an outside auditor. The person who runs a process, or who built a control, should not audit it. Certification auditors check that you defined the competence your internal auditors need and that they have it.
Each finding against a control should name the control and say whether the Statement of Applicability still holds. A nonconformity in a control marked implemented means the status, and the risk it treats, need review. A finding in a control marked not applicable questions the exclusion. Certification auditors compare the SoA with what they see, so fix the SoA before they do.
Yes. Amendment 1:2024 to ISO/IEC 27001:2022, published in February 2024, adds to clause 4.1 a decision on whether climate change is a relevant issue for the ISMS, and to clause 4.2 a note that interested parties can have climate-related requirements. Your internal audit should find that decision and its reasoning, whatever the conclusion.